Most cyberattacks are loud. Ransomware locks your screens and demands payment. A DDoS attack knocks your website offline within minutes. You know something is wrong almost immediately.
Advanced Persistent Threats (APTs) are the opposite. They are quiet, patient, and deliberately invisible. An APT attacker doesn’t want you to notice them, because the longer they stay hidden, the more they can steal. Some organizations discover an APT only after attackers have been inside their network for months, or even years.
In this deep dive, we’ll explain what an APT is, how these attacks unfold, who is behind them, and what your organization can do to defend against them.
What is an Advanced Persistent Threat
An Advanced Persistent Threat is a prolonged, targeted cyberattack in which a skilled adversary gains unauthorized access to a network and remains undetected for an extended period. The goal is usually not immediate disruption but long-term access: stealing intellectual property, spying on communications, or positioning for future sabotage.
The name breaks down neatly into three parts:
Advanced: The attackers use sophisticated techniques, often combining custom malware, zero-day exploits, social engineering, and legitimate administrative tools. They adapt their methods to the specific target.
Persistent: The attackers are in it for the long haul. They establish multiple footholds, maintain access over time, and return even after being partially removed. If one door closes, they already have another one open.
Threat: Behind every APT is a coordinated, well-resourced human operation, not an automated script. These groups have clear objectives, funding, and the patience to pursue them.
The term was popularized by the U.S. Air Force in the mid-2000s to describe state-sponsored intrusions, but today it covers a broader range of attackers, including organized cybercrime groups operating with nation-state-level sophistication.
How APTs Differ from Ordinary Cyberattacks
Understanding the difference helps explain why traditional defenses often fail against APTs.
A typical opportunistic attack casts a wide net. Attackers send millions of phishing emails or scan the internet for any vulnerable server, hoping to hit whoever is unprepared. The attack is fast, automated, and usually noisy.
An APT is the reverse. The attackers select a specific organization in advance, research it thoroughly, and craft their approach to fit. They move slowly to avoid triggering alerts, blend into normal network traffic, and often use the organization’s own tools against it. Where a smash-and-grab criminal wants a quick payout, an APT operator wants a permanent, invisible presence.
This is why APTs are so dangerous: security tools designed to catch known malware or obvious anomalies are frequently blind to an attacker who looks like a legitimate user.
The APT Lifecycle: How an Attack Unfolds
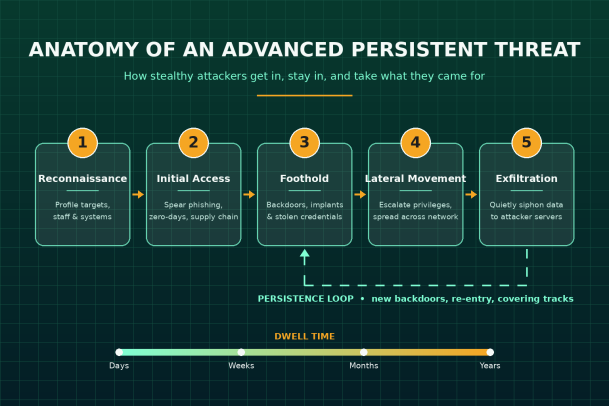
While every campaign is different, most Advanced Persistent Threats follow a recognizable sequence of stages.
1. Reconnaissance
Before launching anything, attackers study their target. They map the organization’s structure, identify key employees on LinkedIn and company websites, catalogue the technologies in use, and look for weak points such as unpatched systems or exposed services. This phase can take weeks.
2. Initial Access
Armed with research, the attackers break in. The most common method is spear phishing: a highly personalized email that appears to come from a trusted colleague, partner, or vendor. Other entry points include exploiting zero-day vulnerabilities, compromising third-party software in a supply chain attack, or using stolen credentials bought on underground markets.
3. Establishing a Foothold
Once inside, attackers install backdoors, remote access tools, or custom implants that let them return at will. They frequently harvest credentials at this stage so they can log in as legitimate users rather than relying on malware alone.
4. Privilege Escalation and Lateral Movement
A single compromised laptop is rarely the prize. Attackers escalate their privileges, often aiming for domain administrator access, and move laterally across the network toward high-value systems such as databases, file servers, email systems, and executive accounts. They commonly use built-in tools like PowerShell, Remote Desktop, and Windows Management Instrumentation, a technique known as “living off the land,” which makes their activity hard to distinguish from normal IT work.
5. Data Exfiltration
With access to valuable data, attackers begin siphoning it out, usually in small, encrypted batches disguised as ordinary traffic so they don’t trip data loss alerts.
6. Persistence and Covering Tracks
This is what makes an APT “persistent.” Attackers deploy redundant backdoors, clear logs, and sometimes go dormant for long periods. Even if defenders discover and remove one entry point, the attackers can re-enter through another. The time between initial compromise and detection is known as dwell time, and every extra day gives the adversary more opportunity to cause damage.
Who is Behind Advanced Persistent Threats
APT groups generally fall into a few categories:
Nation-state actors are the classic APT operators. They pursue espionage, intellectual property theft, political intelligence, and infrastructure sabotage. Security researchers track these groups under names such as APT28 (Fancy Bear), APT29 (Cozy Bear), APT41, and the Lazarus Group.
State-sponsored or state-tolerated criminal groups blur the line between espionage and profit, conducting financially motivated attacks while also serving government interests.
Sophisticated cybercriminal organizations increasingly adopt APT-style tactics, quietly infiltrating networks for long periods before deploying ransomware or extorting victims with stolen data.
Notable APT Examples
A few landmark incidents show the scale and impact of APTs:
Stuxnet (discovered 2010): A highly sophisticated worm that targeted industrial control systems at an Iranian nuclear facility, physically damaging centrifuges. It demonstrated that cyberattacks could cause real-world destruction.
APT1 (exposed 2013): Security firm Mandiant published a landmark report linking a long-running espionage campaign against more than 140 organizations to a Chinese military unit, revealing the industrial scale of state-backed data theft.
SolarWinds (discovered 2020): Attackers compromised the build process of a widely used IT management product, inserting a backdoor into legitimate software updates. Thousands of organizations installed the tainted update, and the attackers selectively exploited high-value targets, including government agencies.
Each of these campaigns went undetected for a significant period, which is exactly what made them so damaging.
Who is at Risk
It’s a mistake to think APTs only target governments and defense contractors. Common targets include:
- Government agencies and critical infrastructure (energy, water, telecommunications)
- Healthcare and pharmaceutical organizations holding valuable research
- Financial services institutions
- Technology and manufacturing companies with proprietary intellectual property
- Law firms, consultancies, and managed service providers with privileged access to clients
Small and mid-sized businesses are also at risk, often not as the final target but as a stepping stone. Attackers compromise a smaller supplier or partner to gain trusted access to a larger organization.
Warning Signs of an APT
Because APTs are designed to stay hidden, detection depends on spotting subtle anomalies. Watch for:
- Unusual login activity, such as logins at odd hours or from unexpected locations, especially for privileged accounts
- Unexpected outbound data flows, including large or regular transfers to unfamiliar external servers
- Backdoor trojans and unknown executables found on multiple endpoints
- Anomalous use of admin tools like PowerShell or remote access utilities by accounts that don’t normally use them
- Unusual data staging, where large volumes of files are compressed or gathered in unexpected locations before exfiltration
Any one of these may have an innocent explanation. Together, they can reveal an attacker who has been operating quietly for some time.
How to Defend Against Advanced Persistent Threats
No single tool stops an APT. Effective defense requires layered security that assumes attackers may already be inside.
Adopt a Zero Trust approach. Never automatically trust any user, device, or file, even inside your network. Verify continuously and grant only the minimum access needed.
Contain unknown files before they can act. Traditional antivirus relies on recognizing known threats, but APTs often use custom or never-before-seen malware. Isolating unknown executables so they can’t modify systems or reach sensitive data closes the gap that signature-based tools leave open.
Deploy Endpoint Detection and Response (EDR). EDR gives you continuous visibility into endpoint behavior, helping you spot suspicious activity like credential dumping or lateral movement.
Invest in 24/7 monitoring. APT operators often act at night or on weekends when they assume no one is watching. Managed Detection and Response (MDR) services provide round-the-clock expert threat hunting.
Harden identities. Enforce multi-factor authentication, limit privileged accounts, and monitor administrative activity closely.
Train your people. Spear phishing remains the most common entry point. Regular, realistic security awareness training makes employees a stronger first line of defense.
Patch and segment. Keep systems updated, and segment networks so that a breach in one area can’t easily spread to your most critical assets.
Final Thoughts
Advanced Persistent Threats represent the most patient and determined adversaries in cybersecurity. They succeed not through brute force but through stealth, persistence, and careful planning. The organizations that defend best against them are the ones that stop relying on detection alone and instead prevent unknown threats from ever gaining a foothold, while keeping constant watch for the subtle signs of an intruder.
The cost of an APT isn’t measured only in stolen data. It’s measured in lost intellectual property, damaged reputation, regulatory penalties, and the long, expensive process of rooting out an attacker who has made themselves at home.
Stop APTs Before They Take Hold
Xcitium’s Zero Trust platform combines patented auto-containment technology, advanced EDR, and 24/7 Managed Detection and Response to neutralize unknown threats before they can cause harm. Unknown files run in isolation, so even never-before-seen malware can’t establish the foothold that APT attackers depend on.
Don’t wait months to discover an intruder in your network. See how Xcitium can help you shut down Advanced Persistent Threats from day one.
Please give us a star rating based on your experience.

 (25 votes, average: 2.20 out of 5, rated)