Every modern IT environment runs on virtual machines, from enterprise data centers to public cloud platforms to a security analyst’s malware lab. Yet many decision-makers still treat virtualization as a background technology, something the infrastructure team handles. That’s a missed opportunity. Knowing what a virtual machine is, how it works, and where its security strengths and weaknesses lie helps IT leaders make better decisions about cost, resilience, and risk.
This guide explains virtual machines in plain language, then goes deeper into the architecture, business benefits, security implications, and best practices that matter most to IT and cybersecurity professionals.
What Is a Virtual Machine?
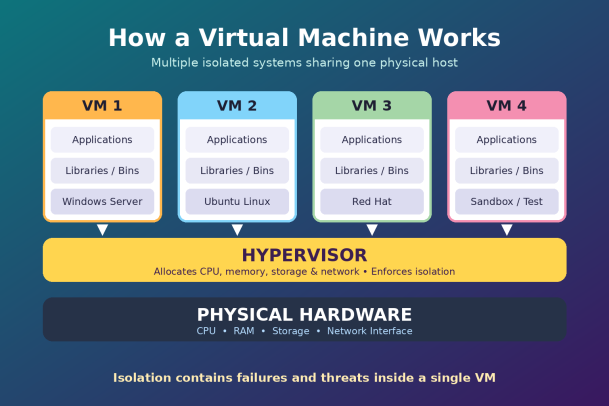
A virtual machine (VM) is a software-based computer that runs on a physical computer. It has its own virtual CPU, memory, storage, and network interface, and it runs its own operating system and applications. From the inside, a VM behaves almost exactly like a physical server or workstation. From the outside, it’s just a set of files and processes managed by the host system.
The key idea is abstraction. Virtualization separates the operating system and applications from the underlying hardware. That separation lets one physical machine run many independent VMs at the same time, each isolated from the others. One server might host a Windows Server VM running Active Directory, a Linux VM running a web application, and a third VM used as a sandbox for testing suspicious files, all without interfering with each other.
How Does a Virtual Machine Work?
The engine behind every VM is the hypervisor, a layer of software that sits between the physical hardware and the virtual machines. The hypervisor allocates physical resources such as CPU cycles, RAM, storage, and network bandwidth to each VM, and it enforces the boundaries that keep VMs isolated from one another.
There are two main types of hypervisors.
Type 1 (bare-metal) hypervisors run directly on the physical hardware with no host operating system underneath. Examples include VMware ESXi, Microsoft Hyper-V, and KVM. Because they have direct hardware access and a small footprint, Type 1 hypervisors are the standard choice for enterprise data centers and cloud providers. They deliver better performance and a smaller attack surface.
Type 2 (hosted) hypervisors run as applications on top of a regular operating system. Examples include Oracle VirtualBox, VMware Workstation, and Parallels Desktop. They’re common for development, training, and security research on individual workstations, where convenience matters more than raw performance.
Each VM is made up of a few core components: a virtual disk file that stores the guest operating system and data, a configuration file that defines its virtual hardware, and runtime memory state. Because a VM is essentially a collection of files, it can be copied, backed up, moved between hosts, or rolled back to an earlier snapshot. That portability is one of virtualization’s most powerful features.
Virtual Machines vs. Containers
IT leaders often ask how VMs compare to containers such as Docker. Both provide isolation, but they work at different levels.
A VM virtualizes the hardware, so every VM includes a full guest operating system. A container virtualizes the operating system, so containers share the host’s kernel and package only the application and its dependencies. Containers are lighter and start in seconds, which makes them ideal for microservices and cloud-native development. VMs offer stronger isolation because each one has its own kernel, which makes them better suited to running different operating systems, legacy applications, and workloads with strict security boundaries.
In practice, most organizations use both. Containers frequently run inside VMs, combining the agility of containers with the isolation of virtual machines.
Why Virtual Machines Matter to IT Leaders
Virtualization isn’t just a technical convenience. It shapes budgets, agility, and business continuity.
Server consolidation and cost savings. Before virtualization, physical servers often ran at a small fraction of their capacity. VMs let organizations consolidate many workloads onto fewer machines, cutting hardware purchases, power, cooling, and data center space.
Faster provisioning. Spinning up a new server once meant ordering hardware and waiting weeks. With VMs and templates, teams can deploy a fully configured server in minutes, which speeds up projects and supports DevOps practices.
Business continuity and disaster recovery. Because VMs are files, they can be replicated to a secondary site or the cloud. If a host fails, workloads can restart elsewhere quickly. Features like live migration let administrators move running VMs between hosts with no downtime during maintenance.
Legacy application support. Many organizations depend on older software that only runs on outdated operating systems. VMs keep those applications running on modern hardware while containing them in a controlled environment.
Foundation for cloud computing. Public cloud services like AWS EC2, Azure Virtual Machines, and Google Compute Engine are built on virtualization. Understanding VMs is essential for planning hybrid and multi-cloud strategies.
Why Virtual Machines Matter to Cybersecurity Professionals
For security teams, virtual machines are both a powerful defensive tool and a significant part of the attack surface.
VMs as a Security Asset
Isolation and containment. The defining security benefit of a VM is isolation. If malware compromises one VM, the hypervisor’s boundaries are designed to stop it from spreading to other VMs on the same host. This principle of running untrusted code in a contained environment underpins modern sandboxing.
Malware analysis and sandboxing. Security researchers use VMs to detonate suspicious files safely, watch their behavior, and collect indicators of compromise without risking production systems. When the analysis is done, the VM can be reverted to a clean snapshot in seconds.
Secure testing environments. VMs let teams test patches, configuration changes, and incident response playbooks in replicas of production before rolling them out.
Rapid recovery. Clean VM snapshots and backups give organizations a reliable way to restore systems after ransomware or other destructive attacks, provided those backups are themselves protected from tampering.
Virtual desktop infrastructure (VDI). Hosting desktops as VMs in the data center keeps sensitive data off endpoints, which is valuable for remote workforces and contractors.
VMs as a Security Risk
Virtualization also introduces risks that security leaders can’t ignore.
Hypervisor attacks. The hypervisor is a high-value target. A vulnerability that allows a “VM escape,” where an attacker breaks out of a guest VM to reach the hypervisor or other VMs, can compromise every workload on a host. Ransomware groups have increasingly targeted hypervisors such as VMware ESXi directly, encrypting many virtual machines in a single strike.
VM sprawl. Because VMs are so easy to create, organizations often lose track of them. Forgotten, unpatched VMs become easy entry points for attackers.
Snapshot and image exposure. VM disk files and snapshots can contain sensitive data, credentials, and memory contents. If they’re stolen or poorly secured, attackers can extract that information offline.
Misconfiguration. Overly permissive virtual networks, weak management console access, and shared resources configured carelessly can undermine the isolation that makes VMs valuable.
Evasion by advanced malware. Some malware detects when it’s running in a VM or sandbox and stays dormant to avoid analysis, then activates once it reaches a real endpoint. That’s why VM-based sandboxing alone isn’t a complete defense.
Best Practices for Securing Virtual Machines
Securing a virtualized environment takes deliberate effort across the hypervisor, the guest systems, and the management layer.
Harden and patch the hypervisor. Apply vendor security updates promptly, disable unneeded services, and follow hardening guides from your hypervisor vendor and frameworks like CIS Benchmarks.
Lock down management access. Restrict access to hypervisor management consoles with multi-factor authentication, role-based access control, and dedicated management networks that are kept separate from user traffic.
Maintain a complete VM inventory. Track every VM, its owner, its purpose, and its patch status. Decommission VMs that are no longer needed to reduce sprawl.
Segment virtual networks. Use micro-segmentation and virtual firewalls to control traffic between VMs, so a compromise in one workload can’t move laterally with ease.
Protect every guest operating system. Each VM needs the same endpoint protection, patching, and monitoring as a physical machine. Virtualization doesn’t make a guest OS secure on its own.
Encrypt and secure VM files. Encrypt virtual disks and snapshots, and store backups in immutable or isolated locations so ransomware can’t reach them.
Monitor continuously. Collect logs from hypervisors and guest systems, and feed them into your SIEM or XDR platform to detect suspicious behavior early.
The Bigger Lesson: Isolation Is a Security Strategy
The most important takeaway for IT and security leaders is that the concept at the heart of virtualization, isolation, is one of the most effective security principles available. A VM limits the blast radius of failures and attacks by keeping workloads separated.
Forward-looking security platforms apply that same principle at the endpoint. Rather than trying to decide in an instant whether an unknown file is safe or malicious, and risking a wrong guess, they run unknown files in a virtualized, isolated environment where they can’t harm the real system. Legitimate applications keep working normally while threats are contained before they can cause damage. This approach closes the gap that detection-only tools leave open, including the zero-day threats and evasive malware that traditional sandboxes miss.
Conclusion
So, what is a virtual machine? It’s a software-defined computer that runs on shared physical hardware, managed by a hypervisor that keeps each system isolated. For IT leaders, VMs deliver consolidation, agility, and resilience. For cybersecurity professionals, they offer powerful tools for containment, analysis, and recovery, while also creating new targets that require careful hardening and monitoring.
Organizations that understand both sides of virtualization are better equipped to build infrastructure that’s efficient, scalable, and secure. And those that extend the principle of isolation to every endpoint gain a decisive advantage against modern threats.
Stop Threats Before They Cause Damage
Xcitium brings the power of isolation to your endpoints. Its patented containment technology automatically runs unknown files in a secure virtual environment, so zero-day malware and ransomware can’t reach your systems, while your users keep working without interruption. See how Xcitium can help your organization move from detection to true prevention.
Please give us a star rating based on your experience.


 (14 votes, average: 2.36 out of 5, rated)