When most organizations picture a cyberattack, they imagine a faceless hacker breaking in from the outside. Yet some of the most damaging breaches start with someone who already has a badge, a login, and the trust of the business. Employees, contractors, and partners hold the keys to sensitive systems every day, and that access can be misused, mishandled, or hijacked.
So, what is an insider threat, and why has it become one of the toughest security challenges for modern businesses? In this guide, we break down the definition, the main types of insider threats, the warning signs to watch for, and the practical steps your organization can take to prevent internal cyber risks before they turn into costly incidents.
What is an Insider Threat
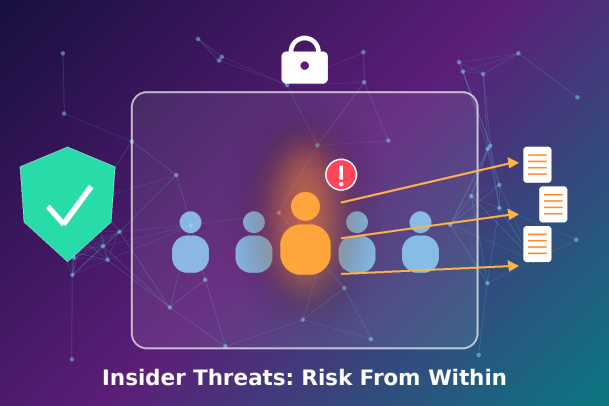
An insider threat is a security risk that originates from within an organization. It involves a person who has, or once had, authorized access to company networks, systems, data, or facilities and who uses that access, intentionally or unintentionally, in a way that harms the organization.
The word “insider” covers more than full-time employees. It can include contractors, temporary staff, vendors, business partners, interns, and even former employees whose accounts were never fully deprovisioned. What makes these individuals different from external attackers is simple: they don’t need to break in. They are already trusted, they know where valuable data lives, and their activity often looks like normal business.
Insider threats can lead to data theft, intellectual property loss, fraud, sabotage of systems, regulatory penalties, and serious reputational damage. Because the actions come from legitimate accounts, they frequently slip past traditional perimeter defenses such as firewalls and basic antivirus tools.
Types of Insider Threats
Not every insider threat involves a disgruntled employee plotting revenge. Understanding the different categories helps security teams design the right controls for each.
1. Malicious Insiders
Malicious insiders deliberately misuse their access to cause harm or gain personally. Their motives range from financial gain and corporate espionage to revenge after a demotion or termination. Common examples include selling customer data, stealing trade secrets before joining a competitor, or planting code that sabotages systems.
2. Negligent or Careless Insiders
This is the most common type of insider threat. Negligent insiders have no intention of causing harm, but their mistakes open the door to attackers. Clicking on a phishing link, reusing weak passwords, emailing sensitive files to the wrong person, or misconfiguring a cloud storage bucket can all expose critical data.
3. Compromised Insiders
A compromised insider is a legitimate user whose credentials or device have been taken over by an external attacker. The employee may have no idea their account is being used. Because the attacker operates under a trusted identity, malicious activity can blend in with everyday work for weeks or months.
4. Third-Party Insiders
Vendors, suppliers, consultants, and managed service providers often receive privileged access to systems. If their own security is weak, or if access isn’t properly limited and monitored, they can become a direct path into your environment.
Why Insider Threats Are So Dangerous
Insider threats are uniquely difficult to detect and contain. Insiders already sit inside the trusted zone, so they bypass many of the defenses built to keep outsiders out. They know which systems hold the most valuable information and how internal processes work, which makes their actions more targeted. Their activity is also easy to mistake for routine work: downloading files, accessing databases, or sharing documents are everyday tasks.
The longer an incident goes undetected, the more it costs. Investigation, remediation, legal fees, regulatory fines, and lost customer trust all add up, and insider incidents are often discovered late precisely because nothing looks out of place at first glance.
Warning Signs of an Insider Threat
While no single behavior proves wrongdoing, certain patterns should prompt a closer look:
- Unusual access patterns, such as logging in at odd hours or from unexpected locations.
- Accessing data outside normal job duties, especially sensitive financial, HR, or customer records.
- Large or unusual data transfers to personal email, USB drives, or unapproved cloud storage.
- Repeated attempts to escalate privileges or bypass security controls.
- Installing unauthorized software or tools that hide activity.
- Behavioral changes, such as open frustration with the company, sudden financial stress, or an upcoming resignation.
- Activity from dormant or former-employee accounts that should no longer be active.
Combining technical signals with HR and behavioral context gives security teams the clearest picture without jumping to conclusions about individuals.
How to Prevent Insider Threats: Best Practices
Preventing insider threats requires a layered approach that blends people, processes, and technology. Here are the most effective steps organizations can take.
Enforce the Principle of Least Privilege
Give every user only the access they need to do their job, and nothing more. Review permissions regularly, remove access promptly when roles change, and limit administrative rights to a small, closely monitored group.
Strengthen Identity and Access Management
Use multi-factor authentication (MFA) across all critical systems so that stolen passwords alone aren’t enough. Centralize identity management, enforce strong password policies, and automate onboarding and offboarding so departing employees and contractors lose access on their last day.
Monitor User Activity and Behavior
User and entity behavior analytics (UEBA) establishes a baseline of normal activity and flags deviations, such as an accountant suddenly downloading engineering files at midnight. Continuous monitoring helps catch both malicious insiders and compromised accounts early.
Protect Sensitive Data at the Source
Classify your data so you know what matters most. Data loss prevention (DLP) tools, encryption, and controls on USB devices and personal cloud storage make it much harder for sensitive information to leave the organization unnoticed.
Secure Every Endpoint
Laptops, desktops, and servers are where insiders actually work and where compromised accounts are exploited. Strong endpoint protection with containment and detection-and-response capabilities stops unknown or malicious files from causing damage, even when they’re launched by a trusted user.
Build a Security-Aware Culture
Since negligence drives so many incidents, regular security awareness training is essential. Teach employees to spot phishing, handle data safely, and report suspicious activity without fear. A positive culture where people feel heard also reduces the resentment that can motivate malicious insiders.
Create an Insider Threat Program and Response Plan
A formal program brings together security, IT, HR, and legal teams. Define clear policies, set escalation paths, and prepare an incident response plan so your team knows exactly how to investigate and contain an insider incident when it happens.
The Role of Zero Trust in Stopping Insider Threats
Traditional security assumed that anything inside the network could be trusted. Insider threats prove that assumption wrong. A Zero Trust approach flips the model: never trust, always verify. Every user, device, and application must continuously prove it should have access, regardless of where it sits.
Under Zero Trust, access is granted per request, sessions are monitored, and suspicious behavior triggers additional verification or automatic containment. Combined with endpoint protection that isolates unknown files before they can execute harmful actions, Zero Trust dramatically shrinks the damage any single insider, careless, malicious, or compromised, can cause.
Conclusion
So, what is an insider threat? It’s the risk that someone you already trust, through malice, mistakes, or a stolen identity, becomes the source of a breach. Because insiders operate with legitimate access, these threats are harder to spot and often more costly than external attacks.
The good news is that insider risk can be managed. By enforcing least privilege, strengthening identity controls, monitoring behavior, securing endpoints, and building a security-aware culture, organizations can detect warning signs early and stop internal cyber risks before they escalate.
Protect Your Organization from the Inside Out
Don’t wait for an insider incident to expose the gaps in your defenses. Xcitium’s Zero Trust endpoint security, real-time containment, and managed detection and response help you neutralize threats from every direction, including the ones already inside your network.
Request a Demo with Xcitium and see how you can stop insider threats before they become breaches.
Please give us a star rating based on your experience.


 (22 votes, average: 2.32 out of 5, rated)