Passwords have been the front door to our digital lives for more than half a century, and they have never been a very good lock. People reuse them, forget them, write them on sticky notes and hand them to convincing phishing pages. Stolen and weak credentials remain one of the most common ways attackers get into accounts and corporate networks, year after year.
That is why so many security teams, browser makers and platform vendors are rallying around a new approach. If you have been asking what is a passkey, and whether it can really replace the password, this guide explains how the technology works, why it is so much harder to steal, where its limits are, and how organizations can start adopting it.
What is a Passkey
A passkey is a passwordless login credential that lets you sign in to a website or app using the same method you use to unlock your device: a fingerprint, a face scan, a PIN or a screen-lock pattern. There is nothing to type, nothing to remember and nothing that can be read aloud to a scammer.
Under the hood, a passkey is a pair of cryptographic keys built on the FIDO2 and WebAuthn standards, developed by the FIDO Alliance and the World Wide Web Consortium (W3C). Apple, Google and Microsoft all support these standards across their operating systems and browsers, which is why passkeys now work on most modern phones, tablets and computers.
Passkeys can live in two places:
- Synced passkeys are stored in a password manager or platform keychain (such as iCloud Keychain or Google Password Manager) and sync across your devices, so a new phone does not mean a new login.
- Device-bound passkeys stay on one piece of hardware, such as a FIDO2 security key, and never leave it. Many regulated industries prefer these for high-privilege accounts.
How Do Passkeys Work
Passkeys rely on public-key cryptography, the same proven math that secures HTTPS connections and digital signatures. Every passkey is made of two linked keys: a private key that stays on your device and a public key that the website stores. What one key locks, only the other can unlock.
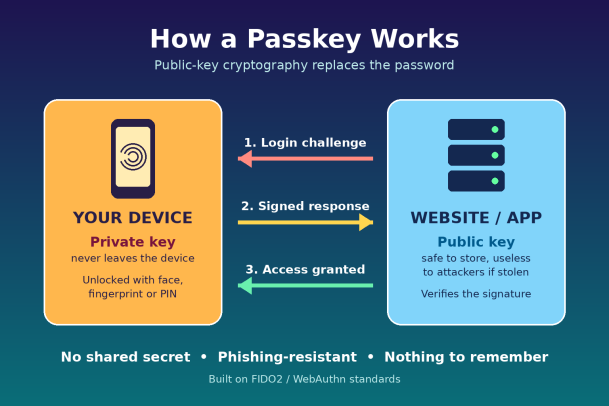
Registration. When you create a passkey for an account, your device generates a brand-new key pair for that specific site. The private key is saved securely on your device or in your password manager. Only the public key is sent to the service.
Login. When you sign in, the following happens in a fraction of a second:
- The website sends your device a random, one-time challenge.
- You unlock the passkey with your face, fingerprint or device PIN.
- Your device signs the challenge with the private key and sends the signature back.
- The website checks the signature against the public key it stored. If it matches, you are in.
Your biometric data never leaves your device and is never shared with the website. It only unlocks the private key locally. Just as important, each passkey is tied to the exact domain it was created for, so your device will refuse to use it on a lookalike phishing site.
Passkeys vs. Passwords vs. Traditional MFA
Passkeys are not just a more convenient password. They remove the shared secret that makes passwords so easy to steal, and they close gaps that many forms of multi-factor authentication (MFA) leave open.
| Factor | Passwords | Password + SMS/OTP MFA | Passkeys |
|---|---|---|---|
| Something to remember | Yes | Yes | No |
| Secret stored on the server | Password hash | Password hash | Public key only |
| Phishing resistance | None | Weak (codes can be relayed) | Strong (domain-bound) |
| Exposed in a server breach | Yes | Yes | No usable secret |
| Credential stuffing risk | High | Reduced | Eliminated |
| Login speed | Typing required | Typing plus code | One tap or glance |
The key difference is phishing resistance. A one-time code sent by SMS or an authenticator app can still be typed into a fake site and replayed by an attacker in real time. A passkey cannot, because the browser only offers it to the legitimate domain. A passkey also combines two factors in one step: something you have (the device) and something you are or know (your biometric or PIN).
Key Benefits of Passkeys
Passkeys improve security and usability at the same time, which is rare in cybersecurity. Here is what they deliver for users and organizations alike.
- Built-in phishing protection. Because a passkey only works on the site it was created for, fake login pages and adversary-in-the-middle kits have nothing to capture.
- No password database to steal. Servers store only public keys. Even if a service is breached, attackers walk away with data that cannot be used to log in.
- An end to credential stuffing. Every passkey is unique to one account on one site, so reused credentials from old breaches become worthless.
- Faster, simpler sign-ins. Users log in with a glance or a touch. Fewer failed logins means less frustration and fewer abandoned sessions.
- Lower IT and help desk costs. Password resets are one of the most common help desk requests. Passkeys reduce lockouts and reset tickets dramatically.
- Stronger compliance posture. Phishing-resistant authentication aligns with guidance such as NIST SP 800-63 and the zero trust direction set by many governments and regulators.
Challenges and Limitations to Consider
Passkeys are a major step forward, but they are not a silver bullet. A realistic rollout plan accounts for these challenges.
- Account recovery. If a user loses every device holding their passkey, they need a secure way back in. Weak fallback methods, such as SMS codes or security questions, can quietly undo the security gains.
- Mixed ecosystems. Cross-platform syncing has improved a great deal, but moving passkeys between different vendors’ managers can still be uneven for some users.
- Legacy applications. Older enterprise systems, VPNs and custom apps may not support WebAuthn without upgrades or an identity provider in front of them.
- User awareness. Many people still do not know what a passkey is. Clear onboarding prompts and simple explanations make adoption far smoother.
- Compromised endpoints. A passkey protects the login, not the device. If malware takes over an endpoint, an attacker may be able to hijack an already authenticated session. Strong endpoint protection remains essential.
How Organizations Can Start Adopting Passkeys
Major consumer platforms, banks, retailers and SaaS providers already offer passkey sign-in, and most enterprise identity providers now support FIDO2. A phased approach lets you capture the benefits without disrupting the business.
- Audit your authentication landscape. Identify which applications, identity providers and devices already support FIDO2/WebAuthn, and which need upgrades.
- Start with high-risk users. Administrators, finance teams and executives are prime phishing targets. Device-bound passkeys or hardware security keys are a strong fit for them.
- Offer passkeys alongside existing logins. Let users opt in first, then make passkeys the default once adoption grows.
- Harden recovery workflows. Use identity verification and phishing-resistant backups instead of SMS or email resets.
- Educate and measure. Explain the change in plain language, then track enrollment rates, help desk tickets and phishing incidents.
- Retire passwords gradually. As coverage grows, remove password fallbacks for accounts that no longer need them.
Passkeys and Zero Trust: Why Authentication Is Only One Layer
Zero trust security is built on a simple rule: never trust, always verify. Passkeys strengthen the “verify the user” part of that rule better than any password ever could. But zero trust also asks whether the device, the application and every file running on it can be trusted.
Attackers know that logins are getting harder to phish, so they are shifting toward session hijacking, malicious downloads, infostealers and ransomware that run after a user has already signed in. A strong authentication strategy therefore needs to be paired with endpoint protection that stops unknown and malicious code from causing damage, along with continuous detection and response across the environment.
That is where a platform approach makes the difference. Passkeys secure the front door, while advanced endpoint security, containment of unknown files and managed detection and response protect everything behind it.
Frequently Asked Questions
Is a passkey safer than a password? Yes. A passkey cannot be guessed, reused or phished, and the website never stores a secret that attackers could use to log in.
Can a passkey be hacked? The cryptography itself is extremely difficult to break. The realistic risks are weak account recovery and compromised devices, which is why recovery hardening and endpoint security matter.
Does the website see my fingerprint or face? No. Biometrics are checked locally on your device and only unlock the private key. They are never sent to the website.
What happens if I lose my phone? Synced passkeys are restored when you sign in to your platform account on a new device. Device-bound passkeys need a backup key or the service’s recovery process.
Will passkeys completely replace passwords? Not overnight. Most services will run passkeys alongside passwords for years, but the industry is clearly moving toward a passwordless default.
Conclusion
So, what is a passkey? It is a cryptographic credential that replaces the password with something you already have and something you already are. It is faster for users, far harder for attackers to steal or phish, and built on open standards that the biggest technology platforms already support. For organizations, passkeys mean fewer breaches caused by stolen credentials, fewer help desk tickets and a smoother path toward zero trust.
Still, a secure login is only the beginning. Once a user is inside, every endpoint, file and process must be protected from threats that never needed a password in the first place. Pairing passwordless authentication with proactive, zero trust endpoint protection is how modern businesses stay ahead.
Ready to secure every endpoint behind your login? See how Xcitium’s zero trust platform stops unknown threats before they can do damage.
Please give us a star rating based on your experience.


 (19 votes, average: 2.47 out of 5, rated)