A few years ago, talking to a computer in plain language and getting a thoughtful, human-like reply felt like science fiction. Today, it is part of everyday work. People draft emails, summarize reports, write code, and research complex topics by simply typing a question. The technology behind this shift is the large language model, or LLM.
If you have ever asked, “What is LLM?”, you are not alone. The term appears everywhere, from boardroom strategy decks to security briefings. Yet many people still find it unclear what an LLM actually is, how it works, and why it matters so much right now.
This guide answers those questions in plain terms. You will learn what large language models are, how they are built, where they are used, what risks they introduce, and how organizations can adopt them safely, especially from a cybersecurity point of view.
What is LLM? A Simple Definition
An LLM, or large language model, is a type of artificial intelligence trained to understand and generate human language. It learns patterns from enormous amounts of text, including books, articles, websites, and code. With that knowledge, it can answer questions, write content, translate languages, and hold natural conversations.
The name explains the idea:
- Large refers to the scale. These models are trained on billions or even trillions of words and contain billions of internal settings, called parameters, that shape their behavior.
- Language refers to the focus. LLMs are built to work with text, although many modern models also handle images, audio, and documents.
- Model refers to the mathematical system that learns from data and makes predictions.
At its core, an LLM does something surprisingly simple. It predicts the most likely next word, or piece of a word, in a sequence. Repeat that prediction thousands of times, and the result is a full paragraph, a working script, or a detailed answer. Because the model has seen so much language, those predictions often look like real reasoning and understanding.
Well-known examples include Anthropic’s Claude, OpenAI’s GPT models, Google’s Gemini, and Meta’s Llama family. Each is built differently, but all share the same foundation.
How Do Large Language Models Work
You do not need a data science degree to understand the basics. Most LLMs are built in four stages.
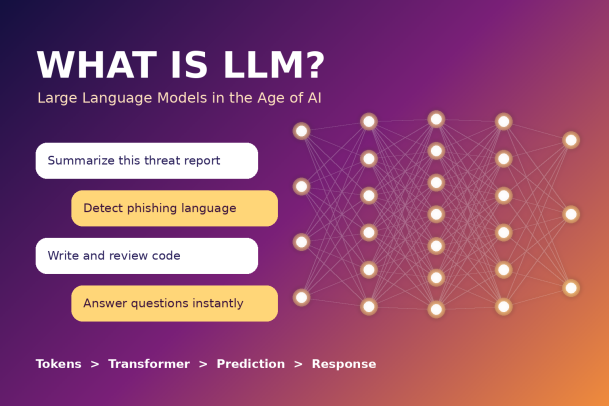
- Tokenization. Text is broken into small units called tokens. A token can be a word, part of a word, or a punctuation mark. The model works with numbers, so each token is converted into a numerical form it can process.
- The transformer architecture. Nearly every modern LLM is based on the transformer, a design introduced by Google researchers in 2017. Its key feature, called attention, lets the model weigh how each word relates to every other word in a passage. That is how it understands that “bank” means something different in “river bank” and “bank account.”
- Pre-training. The model reads massive volumes of text and repeatedly guesses the next token. Each time it guesses wrong, it adjusts its parameters slightly. Over billions of examples, it builds a rich picture of grammar, facts, style, and reasoning patterns.
- Fine-tuning and alignment. A raw pre-trained model is powerful but unpredictable. Developers refine it with curated examples and human feedback, a process often called reinforcement learning from human feedback (RLHF). This step teaches the model to follow instructions, stay helpful, and avoid harmful output.
When you type a prompt, the model processes your tokens, applies everything it learned, and generates a response one token at a time. The size of the text it can consider at once is called its context window. Modern models can handle hundreds of thousands of tokens, enough to read entire reports or codebases in a single pass.
What Can LLMs Do? Key Capabilities and Use Cases
Large language models are general-purpose tools. The same model can switch between very different tasks without being rebuilt. Here are the most common ways organizations use them today.
- Content creation. LLMs draft blog posts, product descriptions, marketing copy, and internal communications in seconds.
- Customer support. AI assistants answer routine questions around the clock and hand complex cases to human agents.
- Software development. Developers use LLMs to write, explain, debug, and review code, which speeds up delivery significantly.
- Research and summarization. LLMs condense long reports, contracts, and technical documents into clear key points.
- Translation and localization. They translate text across dozens of languages while keeping tone and context intact.
- Data analysis. Teams ask questions about spreadsheets and databases in plain language instead of writing complex queries.
- AI agents. Newer systems let LLMs take actions, such as browsing the web, using software tools, and completing multi-step tasks on their own.
The common thread is productivity. LLMs remove repetitive work and let people focus on decisions that require human judgment.
LLMs and Cybersecurity: A Double-Edged Sword
For security teams, large language models bring both a powerful ally and a new set of threats. Understanding both sides is essential.
How LLMs Strengthen Security
Security analysts face alert fatigue, staffing shortages, and attacks that move faster every year. LLMs help close that gap. They can summarize threat intelligence, explain suspicious scripts, draft incident reports, and help analysts triage alerts more quickly. They also help detect phishing by spotting manipulative or unusual language in emails and messages.
How Attackers Exploit LLMs
The same capabilities are available to cybercriminals. Attackers use LLMs to write convincing phishing emails without spelling mistakes, impersonate executives, and scale social engineering campaigns. They can also speed up reconnaissance and help less-skilled actors produce more polished attacks.
New Risks Introduced by LLM Adoption
Organizations that deploy LLMs also open new attack surfaces:
- Prompt injection. Attackers hide instructions in documents, websites, or emails that trick an AI system into ignoring its rules or leaking data.
- Data leakage. Employees may paste confidential code, customer records, or strategy documents into public AI tools.
- Insecure integrations. AI agents connected to email, file systems, or business apps can be manipulated into taking harmful actions.
- Shadow AI. Teams adopt unapproved AI tools that security never reviewed, creating blind spots.
- Model supply chain risk. Third-party models, plugins, and datasets may contain hidden weaknesses.
The lesson is clear. LLMs do not replace a strong security foundation. They make one more important than ever.
Limitations of Large Language Models
LLMs are impressive, but they are not flawless. Knowing their limits helps you use them wisely.
- Hallucinations. Models sometimes produce confident answers that are simply wrong. Always verify critical facts.
- Knowledge cutoffs. A model only knows what was in its training data, unless it is connected to search or live data sources.
- Bias. Models can reflect biases present in the text they learned from.
- Limited true understanding. LLMs recognize patterns extremely well, but they do not experience the world as people do.
- Cost and energy use. Training and running large models requires significant computing power.
Best Practices for Adopting LLMs Safely
Businesses do not need to choose between innovation and security. A few practical steps go a long way:
- Create a clear AI usage policy. Define which tools are approved and what data may never be shared with them.
- Keep humans in the loop. Review AI output before it reaches customers, production systems, or critical decisions.
- Limit permissions. Give AI agents only the access they truly need, following the principle of least privilege.
- Protect your endpoints. Most AI-assisted attacks still land on a device, through a malicious file, link, or script. Endpoint protection that stops unknown threats before they execute remains your most important line of defense.
- Monitor and log AI activity. Track how AI tools are used so you can detect misuse early.
- Train your people. Teach employees to spot AI-generated phishing and to use AI tools responsibly.
The Future of LLMs
Large language models are evolving quickly. Models are becoming more capable, more efficient, and better at reasoning through complex problems. Multimodal models now understand images, audio, and video alongside text. AI agents are moving from answering questions to completing real work across business systems.
As these systems gain more autonomy, security will matter even more. The organizations that benefit most will be those that pair AI adoption with strong governance and proven threat prevention.
Conclusion
So, what is LLM? It is a large language model, an AI system trained on vast amounts of text to understand and generate human language. LLMs power chatbots, coding assistants, research tools, and a growing range of autonomous agents. They are reshaping how we work, learn, and communicate.
Yet every powerful technology cuts both ways. The same models that help defenders also help attackers craft smarter phishing, faster malware, and more convincing scams. Embracing AI safely means building on a security foundation that stops threats before they cause damage, whether those threats are written by a human or a machine.
Protect Your Business in the Age of AI
AI-powered threats demand protection that does not rely on recognizing yesterday’s attacks. Xcitium’s Zero Trust approach to endpoint security isolates unknown files and processes before they can do harm, so your organization stays protected even against brand-new, AI-generated threats.
See how Xcitium keeps your endpoints secure while your teams innovate with confidence.
Please give us a star rating based on your experience.

 (224 votes, average: 1.16 out of 5, rated)