Imagine a busy restaurant where a prankster calls every few seconds to book tables that nobody will ever use. The phone line stays jammed, real customers can’t get through, and the business loses money without a single plate being broken. That, in simple terms, is how a Denial of Service attack works in the digital world.
If you have ever wondered what is DoS attack and why security teams take it so seriously, this guide breaks it down. You’ll learn how these attacks work, the most common types, the real damage they cause, and the practical steps organizations can take to stay protected.
What is a DoS Attack
A Denial of Service (DoS) attack is a cyberattack that aims to make a website, server, application, or network unavailable to its intended users. Instead of stealing data or planting malware, the attacker’s goal is disruption. They overwhelm the target with more traffic or requests than it can handle, or they exploit a weakness that causes the system to crash or freeze.
When a DoS attack succeeds, legitimate users experience slow load times, error messages, timeouts, or a complete outage. For an online store, that means lost sales. For a hospital, it can mean delayed access to patient records. For a bank, it can mean customers locked out of their accounts.
The defining feature of a classic DoS attack is that it usually comes from a single source, one machine or one connection. When the attack is launched from many compromised devices at once, it becomes a Distributed Denial of Service (DDoS) attack, which is larger, harder to block, and far more common today.
How Does a DoS Attack Work
Every server, router, and application has finite resources: bandwidth, memory, CPU power, and a limit on how many connections it can hold open at once. A DoS attack is designed to exhaust one or more of those resources.
The process generally follows three stages. First, the attacker floods the target with a surge of traffic or malformed requests. Next, the target’s resources become overloaded as it tries to process everything it receives. Finally, the system can no longer respond to genuine users, and service is denied.
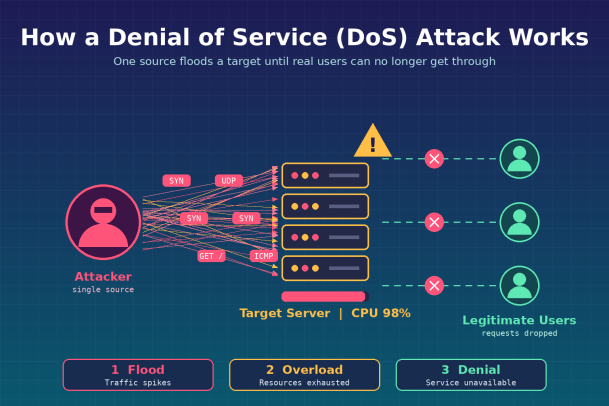
What makes these attacks tricky is that malicious traffic often looks similar to normal traffic. A server can’t always tell the difference between a thousand real shoppers and a thousand fake requests, which is exactly the confusion attackers rely on.
Common Types of DoS Attacks
DoS attacks come in several forms. Understanding them helps security teams recognize warning signs early.
Volume-Based Attacks
These attacks try to consume all the available bandwidth between the target and the wider internet. The attacker sends enormous amounts of data, such as UDP or ICMP packets, so that legitimate traffic simply can’t squeeze through. Think of it as a traffic jam that blocks every lane of the highway.
Protocol Attacks
Protocol attacks exploit weaknesses in how network protocols handle connections. The best-known example is the SYN flood. In a normal TCP connection, a client sends a SYN request, the server replies, and the client confirms. In a SYN flood, the attacker sends a huge number of SYN requests but never completes the handshake. The server keeps those half-open connections waiting until it runs out of room for new ones.
Another example is the Ping of Death, where oversized or malformed packets cause older or unpatched systems to crash.
Application Layer Attacks
Application layer attacks target the software that serves users, such as web servers or APIs. An HTTP flood, for instance, sends a steady stream of seemingly legitimate GET or POST requests to resource-heavy pages like search results or login forms. Because each request looks normal, these attacks are harder to detect and can take down a site using relatively little traffic.
A subtler version is the Slowloris attack, which opens many connections to a web server and keeps them alive by sending partial requests very slowly. The server waits patiently for each request to finish and eventually runs out of available connections.
Buffer Overflow Attacks
In this type, the attacker sends more data to a program than its memory buffer is built to hold. The overflow can crash the application or cause it to behave unpredictably, knocking the service offline.
DoS vs. DDoS: What’s the Difference?
The terms are often used interchangeably, but there is an important distinction.
A DoS attack originates from a single system. Because the traffic comes from one IP address, it is usually easier to identify and block.
A DDoS attack uses a network of compromised devices, often called a botnet, to attack from thousands or even millions of sources at once. These botnets can include infected computers, routers, security cameras, and other Internet of Things (IoT) devices. Blocking one address barely makes a dent, which is why DDoS attacks can reach staggering sizes and last for hours or days.
Both share the same goal: making a service unavailable. The difference lies in scale, complexity, and the difficulty of defending against them.
Why DoS Attacks Are a Serious Cybersecurity Threat
It’s easy to assume that an attack which doesn’t steal data is less dangerous. In reality, the consequences of a DoS attack can be severe and long-lasting.
Financial loss. Every minute of downtime costs money. E-commerce platforms lose sales, SaaS providers may breach service-level agreements, and businesses often spend heavily on emergency response and recovery.
Reputational damage. Customers expect services to be available around the clock. Repeated outages erode trust and can push users toward competitors.
Operational disruption. Internal tools, email systems, and customer support channels may go offline, bringing day-to-day work to a halt.
A smokescreen for other attacks. This is one of the most overlooked dangers. Attackers sometimes launch a DoS attack to distract security teams while they carry out a quieter intrusion, such as deploying ransomware or exfiltrating sensitive data. While everyone is focused on restoring service, the real breach happens in the background.
Extortion. Some criminal groups threaten organizations with a DoS attack unless a ransom is paid, a tactic known as ransom DoS or RDoS.
Warning Signs of a DoS Attack
Detecting an attack early can dramatically reduce its impact. Common indicators include unusually slow network performance, a website or service that suddenly becomes unreachable, a sharp and unexplained spike in traffic from a single IP address or region, a flood of requests to a single page or endpoint, and unusual traffic patterns at odd hours.
Of course, some of these signs can also be caused by legitimate events, like a product launch or a viral social media post. That’s why continuous monitoring and baseline traffic analysis are essential for telling the difference.
How to Prevent and Mitigate DoS Attacks
No organization can guarantee it will never be targeted, but a layered defense strategy makes attacks far less effective.
Monitor Network Traffic Continuously
Understanding what normal traffic looks like allows you to spot anomalies quickly. Real-time monitoring tools can alert teams the moment traffic patterns deviate from the baseline.
Use Rate Limiting and Traffic Filtering
Rate limiting restricts how many requests a single user or IP address can make within a set timeframe. Firewalls and intrusion prevention systems can filter out malformed packets and block known malicious sources before they reach critical systems.
Deploy Web Application Firewalls (WAFs)
A WAF sits in front of web applications and inspects incoming HTTP traffic. It can identify and block application layer attacks like HTTP floods that traditional network firewalls might miss.
Build in Redundancy and Scalability
Distributing services across multiple servers, data centers, or cloud regions ensures that no single point of failure can bring everything down. Content delivery networks (CDNs) and load balancers help absorb and spread out traffic surges.
Keep Systems Patched and Updated
Many protocol and buffer overflow attacks exploit known vulnerabilities. Regular patching closes those gaps and removes easy targets.
Secure Your Endpoints
Botnets are built from poorly secured devices. Strong endpoint protection prevents your own machines from being recruited into attacks against others, and it stops attackers from using a DoS event as cover for a deeper compromise. Advanced solutions that isolate unknown files and processes can neutralize threats before they ever execute.
Create an Incident Response Plan
When an attack hits, speed matters. A documented response plan should define who is responsible for what, how to communicate with customers and stakeholders, and which steps to take to restore service. Running regular drills keeps the team ready.
The Future of DoS Threats
As more devices connect to the internet, the pool of potential botnet recruits keeps growing. Attackers are also becoming more sophisticated, combining multiple attack vectors in a single campaign and using automation to adapt in real time. At the same time, the rise of cloud services and APIs has created new surfaces for application layer attacks.
This evolving landscape means that reactive security is no longer enough. Organizations need proactive, intelligent protection that can detect threats early, contain them automatically, and keep business running without interruption.
Final Thoughts
So, what is DoS attack in a nutshell? It’s a deliberate attempt to overwhelm a system so that the people who rely on it can’t use it. While the concept is simple, the impact on revenue, reputation, and security can be enormous, especially when a DoS attack is used to mask a more dangerous breach.
The good news is that with continuous monitoring, layered defenses, strong endpoint protection, and a clear response plan, organizations can significantly reduce their risk and recover quickly when attacks occur.
Protect Your Business Before the Next Attack Hits
Downtime is expensive, and attackers aren’t waiting. Xcitium’s advanced cybersecurity platform helps you stop threats at the endpoint, contain unknown attacks before they can cause damage, and keep your operations running smoothly, even under pressure.
See how Xcitium can strengthen your defenses against DoS attacks and the threats hiding behind them.
Please give us a star rating based on your experience.

 (22 votes, average: 2.23 out of 5, rated)